Privilege Escalation Using DOP In MacOS
Yoochan Lee (Seoul National University), Jeongsu Choi (Raon WhiteHat), Junoh Lee (Theori), Sangjun Song (Theori)
HITBSecConf2023 - Amsterdam · Day 2 · Track 2
Overview
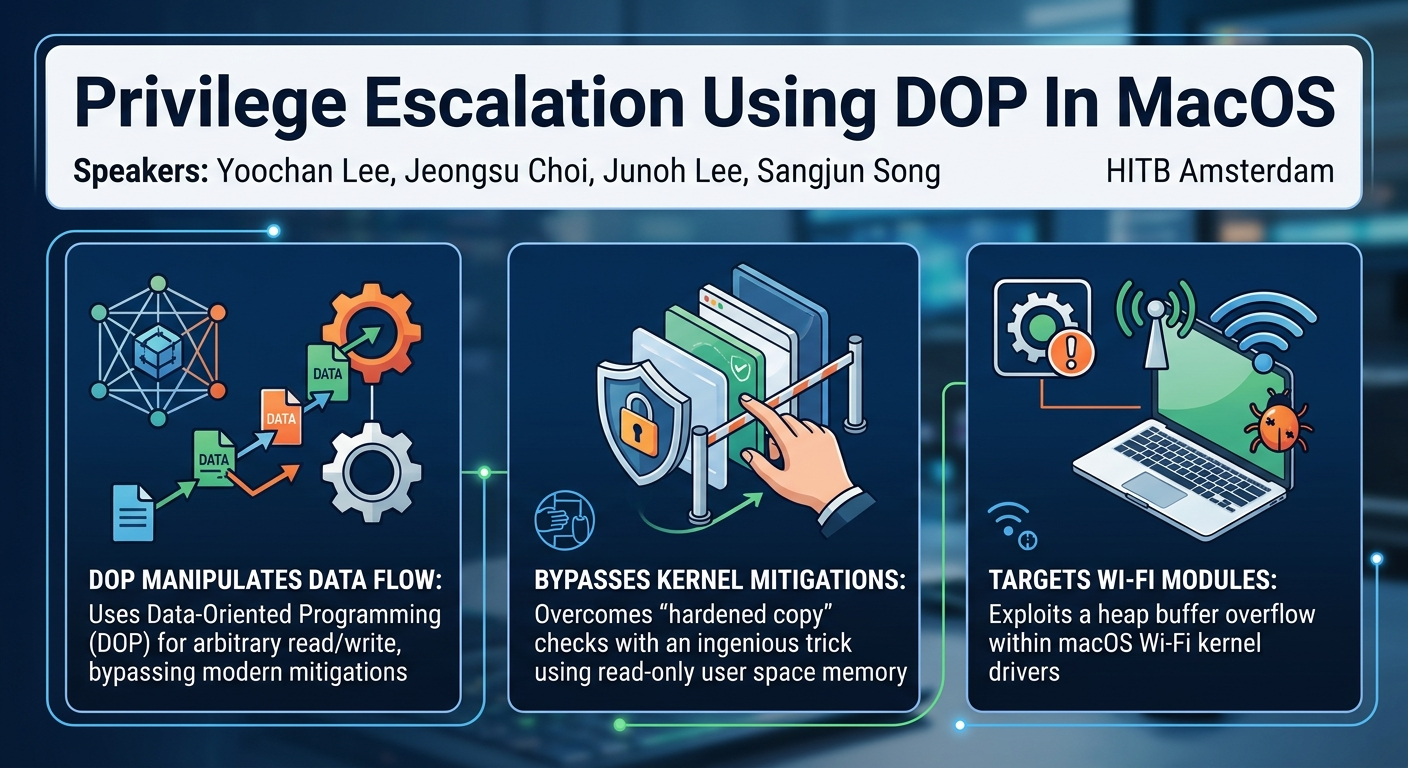
In this insightful presentation from HITB Amsterdam, the research team GYG, comprising Yoochan Lee, Jeongsu Choi, Junoh Lee, and Sangjun Song, unveiled a compelling demonstration of privilege escalation on macOS x8664 using Data-Oriented Programming (DOP). The talk, titled "Privilege Escalation Using DOP In MacOS," delved into a previously unpatched heap buffer overflow vulnerability discovered within the macOS Wi-Fi kernel module. This research highlights the continued relevance of kernel-level vulnerabilities, even in highly secured operating systems, and showcases how advanced exploitation techniques like DOP can bypass modern mitigations.
Key moments
- 4:00 Introduction to Data-Oriented Programming (DOP)
- 6:50 Three Primitives for DOP Privilege Escalation
- 8:00 Hip Buffer Overflow Bug in macOS Wi-Fi Module
- 14:00 Detailed Explanation of the Hip Buffer Overflow
- 18:00 Bypassing Hardened Copy Mitigation for Overflow
- 22:00 Exploiting with ip6popacketinfo Object
- 25:30 Final Privilege Escalation via Cred Object Write
- 26:00 Live Demo of Privilege Escalation
Privilege Escalation Using DOP In MacOS
Speakers: Yoochan Lee (Seoul National University); Jeongsu Choi (Raon WhiteHat); Junoh Lee (Theori); Sangjun Song (Theori)
Conference: HITB Amsterdam
YouTube: https://www.youtube.com/watch?v=C4HiS_2accs
Overview
In this insightful presentation from HITB Amsterdam, the research team GYG, comprising Yoochan Lee, Jeongsu Choi, Junoh Lee, and Sangjun Song, unveiled a compelling demonstration of privilege escalation on macOS x86_64 using Data-Oriented Programming (DOP). The talk, titled "Privilege Escalation Using DOP In MacOS," delved into a previously unpatched heap buffer overflow vulnerability discovered within the macOS Wi-Fi kernel module. This research highlights the continued relevance of kernel-level vulnerabilities, even in highly secured operating systems, and showcases how advanced exploitation techniques like DOP can bypass modern mitigations.
The core of the presentation focused on how a carefully crafted heap buffer overflow in the Wi-Fi driver could be chained with DOP primitives to achieve arbitrary kernel read/write capabilities, ultimately leading to root privileges. The speakers meticulously detailed the vulnerability, the innovative bypass for a "hardened copy" mitigation, and the intricate steps involved in constructing a DOP exploit chain. This work is particularly significant as DOP, while recognized in academia, is often overlooked in industry, yet it proves to be an extremely potent and patch-agnostic method for kernel exploitation.
Background
▶ Watch: Introduction to Data-Oriented Programming (DOP) (4:00)
The landscape of exploit development is a continuous arms race between attackers and defenders, marked by the evolution of both exploitation techniques and security mitigations. The speakers began by tracing this evolution from early kernel exploits that leveraged user-to-kernel memory access (e.g., storing shellcode in user space and redirecting the instruction pointer) to more sophisticated methods. Mitigations like SMEP (Supervisor Mode Execution Prevention) and SMAP (Supervisor Mode Access Prevention) were introduced to prevent kernel code from accessing user-space memory, effectively nullifying these early techniques.
Attackers adapted by moving to direct map regions within the kernel, which mirrored user space but were accessible from the kernel. When these regions had their execute permissions revoked, Return-Oriented Programming (ROP) emerged as the dominant technique, chaining small snippets of existing kernel code (gadgets) to achieve arbitrary execution. To counter ROP, KASLR (Kernel Address Space Layout Randomization) was implemented, randomizing kernel memory layouts and making gadget addresses unpredictable. This necessitated information leakage exploits to de-randomize the kernel's base address. The eventual rise of CFI (Control Flow Integrity) aimed to constrain control flow changes, potentially mitigating ROP entirely.
In this context, Data-Oriented Programming (DOP) is presented as the "latest exploit technique," particularly effective against kernels. Unlike ROP, which manipulates control flow, DOP focuses on manipulating data flow to achieve arbitrary read or write operations. This makes it exceptionally well-suited for kernel exploits, where the primary goal for privilege escalation is often to modify a specific security-critical data structure, such as setting the cred->uid (user ID) to zero. A key strength of DOP highlighted by the speakers is its patch agnosticism. While ROP gadgets are highly sensitive to patches that change code offsets, DOP gadgets (data structures and their manipulation logic) are less affected unless the underlying data structures themselves are altered. For a successful DOP-based privilege escalation, three core primitives are required: information leakage, arbitrary address read, and arbitrary address write.
Key Findings
▶ Watch: Hip Buffer Overflow Bug in macOS Wi-Fi Module (8:00)
The central discovery of this research is a heap buffer overflow vulnerability located within the macOS Wi-Fi kernel module, specifically affecting the io80211 family and the Broadcom kernel extension. This vulnerability, initially found by the team in 2018 and successfully exploited in 2020, remained unpatched and undisclosed to the public at the time of the HITB Amsterdam presentation, though Apple had assigned a CVE number in 2022. The speakers noted that this specific attack surface had been disclosed before (in a GDI blog post based on their prior report), affirming its continued relevance as an attack vector.
The heap buffer overflow manifests in the interaction between the setIE and getIE functions, which are callable from user space via ioctl system calls. The setIE function is responsible for storing Information Elements (IEs), including their length, on the kernel heap. Crucially, this length is stored within the vndr_ie structure. The vulnerability is triggered during the execution of the getIE function. While getIE allocates a new kernel heap buffer with a size specified by the user, the subsequent memory copy operation uses the previously stored length from vndr_ie as its size argument. If the stored length is greater than the user-controlled allocated buffer size, a buffer overflow occurs. For instance, if a buffer of 80 bytes is allocated but 100 bytes are copied, an overflow of 20 bytes happens. The critical aspect here is that both the allocated buffer size and the overflow length are user-controllable.
A significant challenge in exploiting this overflow was bypassing the "hardened copy" mitigation. This mitigation, designed to prevent memory corruption, triggers a kernel panic if a copyout function attempts to copy more data than the size of the target object. Since the overflow inherently requires copying more data than allocated, this mitigation initially seemed to render the exploit impossible. However, the team devised an ingenious bypass: they identified that if the first copyout operation (which occurs before the problematic overflow-causing copy) fails, the second, panic-inducing copyout is never executed. They achieved this by providing a user-space memory address with read-only permissions as the target for the first copyout. This causes the write operation to fail, the copyout function returns an error, and the kernel panic is averted, allowing the subsequent overflow to proceed without triggering the mitigation.
Finally, a key finding enabling the DOP exploit was the identification of a single kernel object, ip6_po_packetinfo, which conveniently provided all three necessary DOP primitives: information leakage, arbitrary address read, and arbitrary address write. This discovery significantly streamlined the exploitation process, as it eliminated the need to chain multiple distinct vulnerabilities or objects for each primitive.
Technical Deep Dive
▶ Watch: Bypassing Hardened Copy Mitigation for Overflow (18:00)
The technical foundation of this exploit lies in a heap buffer overflow within the macOS Wi-Fi driver, specifically within the Broadcom kernel extension. User applications interact with this extension via socket and ioctl calls, targeting functions like setIE and getIE.
- Vulnerability Mechanism:
- When a user calls
setIE, an Information Element (IE) and itslengthare stored in a kernel heap object, specifically within avndr_iestructure. Thislengthfield is user-controlled. - Subsequently, when
getIEis invoked, the kernel allocates a new buffer on the heap. The size of this new buffer is also user-controlled. - The crucial flaw occurs when the kernel then performs a
memory copyfrom the storedvndr_ieto this newly allocated buffer. Instead of using the size of the newly allocated buffer, thememory copyoperation uses thelengthfield stored invndr_ie. - If the user-controlled
lengthinvndr_ieis greater than the user-controlledsizeof the newly allocated buffer, a heap buffer overflow occurs. This allows an attacker to write arbitrary data beyond the bounds of the allocated buffer, corrupting adjacent heap objects.
- Hardened Copy Mitigation Bypass:
- macOS employs a mitigation that causes a kernel panic if
copyoutattempts to write more data than the destination buffer's allocated size. This would normally prevent any heap overflow viacopyout. - The bypass leverages the fact that
getIEtypically involves twocopyoutoperations. The firstcopyoutcopies data to a user-provided buffer, and the second (the one causing the overflow) copies the actual IE data. - The researchers discovered that if the first
copyoutoperation fails, the secondcopyout(which would trigger the kernel panic) is skipped. - To make the first
copyoutfail, the attacker provides a user-space memory address that has been explicitly set with read-only permissions. When the kernel attempts to write to this read-only user-space memory, the operation fails, and thecopyoutfunction returns an error. - This simple yet effective trick prevents the hardened copy mitigation from triggering a kernel panic, allowing the subsequent heap buffer overflow to proceed safely from the attacker's perspective.
- Data-Oriented Programming (DOP) Chain:
- The objective is to achieve arbitrary address read/write to zero out the
cred->uidfor root privileges. This requires three primitives: information leakage, arbitrary read, and arbitrary write. - The chosen target object for corruption is
ip6_po_packetinfo, which is allocated in thekalloc.32zone. This object proved to be highly versatile, providing all three necessary primitives. - Heap Spray and Pointer Corruption:
- To ensure
ip6_po_packetinfois placed immediately after the vulnerable object, the researchers employed heap spraying. They sprayed a significant number ofmach_task_selfobjects into thekalloc.32zone, anticipating thatip6_po_packetinfowould be allocated adjacent to one of them. - The heap buffer overflow is then used to overwrite 17 bytes of the vulnerable object. This precisely corrupts the first byte of an
ip6_po_packetinfopointer, redirecting it to point to a controlledmach_task_selfobject within the sprayed heap. - Information Leakage:
- By manipulating the now-corrupted
ip6_po_packetinfopointer, the attacker can leak the address of theipc_portfrom themach_task_selfobject. This provides a crucial kernel pointer. - Recursive Arbitrary Address Read:
- With arbitrary read capability (via
ip6_po_packetinfo), the attacker then performs a series of reads to traverse kernel structures:
- Leak the
kobjectpointer within theipc_port, which points to thetaskstructure. - Leak the
taskstructure itself. - From the
taskstructure, leak thebsdinfo(process structure) pointer. - From
bsdinfo, leak theucredstructure pointer. - This recursive process ultimately reveals the precise kernel address of the
credobject, which contains the user's privileges.
- Privilege Escalation:
- Finally, using the arbitrary address write primitive (again via the manipulated
ip6_po_packetinfoobject), the attacker writes a0to theuidfield within thecredobject. This effectively changes the process's user ID to root, achieving full privilege escalation.
The entire exploit chain is designed to be highly reliable and efficient, leveraging the specific memory management characteristics of macOS (kalloc zones) and the flexibility of DOP to achieve its objective.
Demo / Proof of Concept
▶ Watch: Exploiting with ip6_po_packetinfo Object (22:00)
The presentation included a demonstration video showcasing the exploit in action. The speakers highlighted the exceptional speed of the Proof of Concept (PoC). They noted that the exploit runs "very fast" because it does not require any sleep functions or other timing-dependent operations, indicating a high degree of reliability and determinism in the exploitation chain.
The video briefly showed the initial user ID, followed by the execution of the exploit. Immediately after, the user ID was checked again, confirming that the privileges had been successfully escalated to root (UID 0). This rapid execution underscores the effectiveness of the DOP technique and the precision with which the heap buffer overflow and subsequent memory manipulations were controlled. The demo served as concrete evidence that the theoretical bypasses and exploitation primitives discussed were fully functional in a real-world macOS environment.
Defensive Implications
▶ Watch: Live Demo of Privilege Escalation (26:00)
This research offers several critical defensive implications for securing macOS and other operating systems against similar advanced exploitation techniques:
- Strengthening Heap Protections: The vulnerability highlights that even with existing mitigations, heap management remains a fertile ground for attackers. Developers should adopt more robust heap metadata integrity checks, implement stronger canary values for heap chunks, and explore mechanisms to detect out-of-bounds writes more aggressively than simple size checks.
- Enhancing
copyin/copyoutHardening: The bypass of the "hardened copy" mitigation demonstrates that assumptions about memory access permissions can be exploited. Kernel APIs designed to transfer data between user and kernel space (copyin,copyout) need more sophisticated validation beyond just size checks. This could involve verifying memory permissions more strictly throughout the entire copy operation or introducing additional integrity checks on the source/destination buffers. - Broader Adoption of Control Flow Integrity (CFI) for Data Flows: While CFI typically focuses on preventing arbitrary control flow transfers (e.g., ROP), DOP circumvents this by manipulating data. Future security mitigations might need to extend CFI-like principles to data flow integrity, ensuring that critical data structures are only modified by legitimate, intended code paths. This is a significantly more complex problem but could be a long-term defense against DOP.
- Improved Kernel Module Isolation and Sandboxing: The vulnerability resides in a Wi-Fi kernel module. Such device drivers, often complex and interacting closely with hardware, present a large attack surface. Implementing stricter compartmentalization for kernel modules, perhaps akin to user-space sandboxing, could limit the blast radius of a successful exploit, preventing it from immediately leading to full kernel compromise.
- Auditing Legacy or Less-Scrutinized Code: The vulnerability was discovered in 2018 and existed in a Wi-Fi driver, a component often rich in legacy code and complex interactions. This suggests that older or less frequently audited kernel modules can harbor critical vulnerabilities. Continuous and thorough security audits, especially for components handling external input like network drivers, are essential.
- Expediting Vulnerability Disclosure and Patching: The extended timeline between discovery (2018), full exploitation (2020), vendor notification, and the lack of public patch notes at the time of the talk (2023) underscores the challenges in vendor response. Faster, more transparent disclosure and patching processes are crucial to protect users.
Key Takeaways
- Data-Oriented Programming (DOP) is a powerful, patch-agnostic kernel exploitation technique, particularly effective for achieving arbitrary read/write primitives and privilege escalation by manipulating data flow.
- macOS Wi-Fi kernel modules (e.g.,
io80211and Broadcom extensions) remain a high-value attack surface, demonstrating that even complex and widely used components can harbor critical vulnerabilities. - Heap buffer overflows, even if seemingly "old," can be successfully exploited against modern operating systems, provided attackers can cleverly bypass contemporary mitigations like "hardened copy" checks.
- An ingenious bypass for "hardened copy" mitigation was demonstrated by intentionally failing an initial
copyoutoperation using read-only user-space memory, preventing a kernel panic and allowing the exploit to proceed. - Identifying a single kernel object (
ip6_po_packetinfo) that provides all three necessary DOP primitives (information leakage, arbitrary read, arbitrary write) significantly simplifies the construction of a full exploit chain. - The entire exploit chain, from heap spray and pointer corruption to recursive arbitrary reads and finally setting
cred->uidto zero, can be executed with exceptional speed and reliability, indicating its practical viability.
About the Speaker(s)
The presentation was delivered by Yoochan Lee, a researcher from Seoul National University, representing the academic side of the team. He was joined by Jeongsu Choi from Raon WhiteHat, and Junoh Lee and Sangjun Song from Theori, bringing industry expertise to the research. Together, they form Team GYG, a group that originally focused on CTF (Capture The Flag) competitions but has expanded its scope to include independent security research and bug hunting. Their diverse backgrounds in both academia and industry contribute to a comprehensive approach to identifying and exploiting vulnerabilities.
Reviews
Dr. Zero (Offensive Security Researcher) — STRONG ACCEPT
Solid kernel exploitation research with a real unpatched vuln, a clever mitigation bypass, and a clean DOP chain. Not groundbreaking technique-wise—DOP isn't new—but the hardened copy bypass is genuinely clever, and the single-object primitive discovery is elegant. This is real work, not a rehash.
Heather Calloway (CISO) — SOLID
Competent kernel exploitation research demonstrating a real macOS privilege escalation via heap overflow and DOP. For most CISOs, this is confirmation that macOS kernel attack surface remains active—worth knowing, but not operationally actionable unless you're running a platform security team or have specific Apple fleet concerns.