TLBlur: Compiler-Assisted Automated Hardening against Controlled Channels on Off-the-Shelf Intel SGX Platforms
Daan Vanoverloop
34th USENIX Security Symposium (USENIX Security '25) · Day 1 · System Security 2: Trusted and Robust Computing
Overview
This groundbreaking research, titled "TORCHLIGHT: Shedding LIGHT on Real-World Attacks on Cloudless IoT Devices Concealed within the Tor Network," uncovers a critical and previously under-explored threat vector: the anonymous exploitation of cloudless Internet of Things (IoT) devices via the Tor network. Authored by a collaborative team from Southeast University, Drexel University, and the University of Massachusetts Lowell, this work highlights a significant shift in the IoT security landscape, where devices once considered secure due to their lack of cloud reliance are now directly exposed to sophisticated, anonymous cyberattacks.
Read the paper · Download the PDF (PDF) · Slides
Paper abstract
The rapidly expanding Internet of Things (IoT) landscape is shifting toward cloudless architectures, removing reliance on centralized cloud services but exposing devices directly to the internet and increasing their vulnerability to cyberattacks. Our research revealed an unexpected pattern of substantial Tor network traffic targeting cloudless IoT devices, suggesting that attackers are using Tor to anonymously exploit undisclosed vulnerabilities (possibly obtained from underground markets). To delve deeper into this phenomenon, we developed TORCHLIGHT, a tool designed to detect both known and unknown threats targeting cloudless IoT devices by analyzing Tor traffic. TORCHLIGHT filters traffic via specific IP patterns, strategically deploys virtual private server (VPS) nodes for cost-effective detection, and uses a chain-ofthought (CoT) process with large language models (LLMs) for accurate threat identification. Our results are significant: for the first time, we have demonstrated that attackers are indeed using Tor to conceal their identities while targeting cloudless IoT devices. Over a period of 12 months, TORCHLIGHT analyzed 26 TB of traffic, revealing 45 vulnerabilities, including 29 zero-day exploits with 25 CVE-IDs assigned (5 CRITICAL, 3 HIGH, 16 MEDIUM, and 1 LOW) and an estimated value of approximately $312,000. These vulnerabilities affect around 12.71 million devices across 148 countries, exposing them to severe risks such as information disclosure, authentication bypass, and arbitrary command execution. The findings have attracted significant attention, sparking widespread discussion in cybersecurity circles, reaching the top 25 on Hacker News, and generating over 190,000 views.
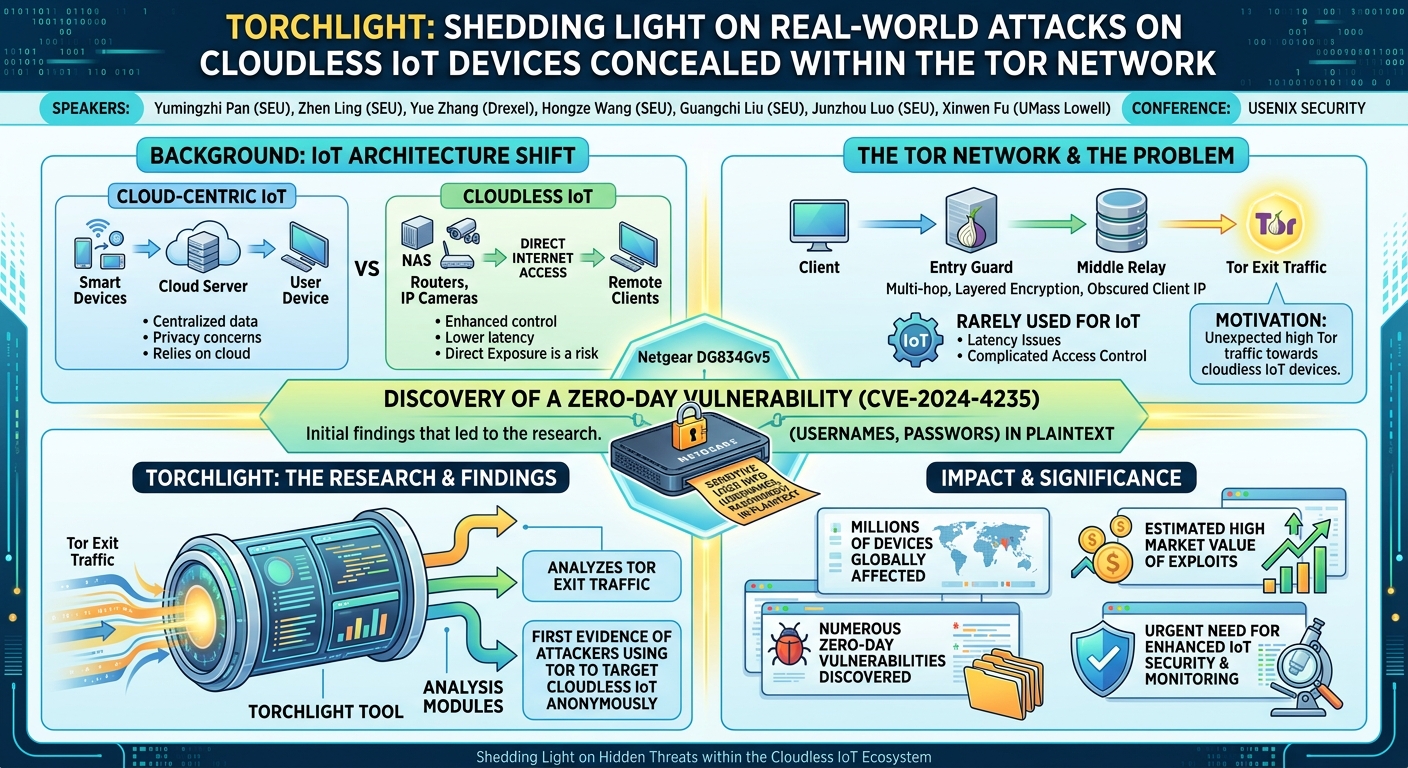
TORCHLIGHT: Shedding LIGHT on Real-World Attacks on Cloudless IoT Devices Concealed within the Tor Network
Speakers: Yumingzhi Pan (Southeast University), Zhen Ling (Southeast University), Yue Zhang (Drexel University), Hongze Wang (Southeast University), Guangchi Liu (Southeast University), Junzhou Luo (Southeast University), Xinwen Fu (University of Massachusetts Lowell)
Conference: USENIX Security
YouTube: N/A (This is a peer-reviewed conference paper, not a recorded talk.)
Overview
This groundbreaking research, titled "TORCHLIGHT: Shedding LIGHT on Real-World Attacks on Cloudless IoT Devices Concealed within the Tor Network," uncovers a critical and previously under-explored threat vector: the anonymous exploitation of cloudless Internet of Things (IoT) devices via the Tor network. Authored by a collaborative team from Southeast University, Drexel University, and the University of Massachusetts Lowell, this work highlights a significant shift in the IoT security landscape, where devices once considered secure due to their lack of cloud reliance are now directly exposed to sophisticated, anonymous cyberattacks.
The significance of this research lies in its novel approach to detecting hidden threats and the alarming scale of its findings. By developing TORCHLIGHT, a sophisticated tool that analyzes Tor exit traffic, the researchers have provided the first clear evidence that attackers are leveraging Tor to conceal their identities while targeting cloudless IoT devices. The discovery of numerous zero-day vulnerabilities impacting millions of devices globally, coupled with the estimated market value of these exploits, underscores the urgent need for enhanced security measures and proactive monitoring in the rapidly expanding cloudless IoT ecosystem.
Background
The Internet of Things (IoT) landscape is undergoing a significant architectural shift from traditional Cloud-Centric IoT to Cloudless IoT. Cloud-Centric IoT systems rely on centralized cloud servers for communication, data processing, and storage, particularly for devices behind Network Address Translation (NAT). While offering convenience and often compensating for devices with limited computational capacity, this model introduces privacy concerns due to sensitive data uploads and reliability issues tied to cloud provider longevity.
In contrast, Cloudless IoT devices, such as network storage devices, surveillance recorders, and routers, operate by directly exposing themselves to the internet, eliminating the need for cloud intermediaries. This architecture offers enhanced direct control, reduced latency, and alleviates user concerns about cloud-related data breaches. However, this direct internet exposure is a double-edged sword, making these devices prime targets for cyberattacks. Cloudless devices typically possess substantial computational capacity, enabling them to provide services like device information, data access, control, and file access directly to remote clients.
The Tor (The Onion Router) network is a decentralized system designed to protect users' communication privacy by routing internet traffic through a series of volunteer-operated relays (Onion Routers or ORs). This multi-hop, layered encryption process obscures the client's real IP address, making it difficult to trace the origin of communications. While celebrated for its anonymity, Tor is rarely used for accessing IoT devices due to the complexities it introduces, such as additional latency and obscured IP addresses, which can disrupt real-time operations and complicate access control.
The motivation for this research stemmed from an unexpected observation: a substantial volume of Tor network traffic directed towards cloudless IoT devices. A targeted analysis involving a Netgear DG834Gv5 router revealed a zero-day vulnerability (later assigned CVE-2024-4235) exposing sensitive user information, including usernames and passwords, in plaintext. This discovery suggested a troubling possibility: attackers might be using Tor to anonymously exploit undisclosed vulnerabilities, potentially acquired from underground markets, without revealing their identities. The core problem statement then became to develop a framework to detect both known and unknown threats targeting cloudless IoT devices by analyzing Tor traffic, focusing on vulnerabilities that enable reconnaissance, data manipulation (excluding modifications), file manipulation, and device manipulation attacks.
Key Findings
The research by Pan et al. presents a compelling case for the active and sophisticated use of the Tor network by attackers to exploit cloudless IoT devices, unveiling a hidden threat landscape. The TORCHLIGHT system, deployed over a 12-month period, analyzed an astounding 26 TB of traffic, leading to several significant and alarming discoveries:
Firstly, and most critically, the study provides clear evidence that numerous attackers are indeed using Tor to conceal their identities while actively targeting cloudless IoT devices. This finding fundamentally challenges previous assumptions about Tor's limited utility in direct IoT exploitation.
Secondly, TORCHLIGHT identified a total of 45 unique vulnerabilities, a substantial portion of which were previously unknown. Specifically, 29 zero-day exploits were discovered, with 25 CVE-IDs assigned to these novel findings. The severity distribution of these assigned CVEs is particularly concerning: 5 CRITICAL, 3 HIGH, 16 MEDIUM, and 1 LOW, indicating a wide range of severe security risks.
Thirdly, the financial and societal impact of these vulnerabilities is substantial. The estimated market value of the discovered exploits, as assessed by VulDB, is approximately $312,000. These vulnerabilities collectively affect an estimated 12.71 million devices across 148 countries, exposing a massive attack surface to various risks including information disclosure, authentication bypass, privilege escalation, and arbitrary command execution. Over 90,047 attack attempts were recorded, demonstrating the persistent efforts of these malicious actors.
The research further revealed that Digital Video Recorders (DVRs) and cameras are the most frequently targeted device types, accounting for 54.9% and 36.5% of identified devices, respectively. Prominent vendors like Qualvision (40.9%), TVT (10.9%), and Hikvision (6.3%) were among the most affected. A concerning trend observed was the targeting of legacy products, such as the D-Link DNS-320L NAS (affected by six zero-day vulnerabilities from a 2018 firmware) and the Netgear DG834Gv5 router (vulnerable since its 2011 firmware release), which often lack modern security features and receive no further updates.
Finally, the findings garnered significant attention within the cybersecurity community, sparking widespread discussion, reaching the top 25 on Hacker News, and generating over 190,000 views, underscoring the critical relevance and impact of this research.
Technical Deep Dive
The TORCHLIGHT system is meticulously designed to overcome significant challenges in detecting anonymous IoT attacks through Tor exit traffic. The authors identified three primary hurdles: (C-1) detecting Tor traffic with limited resources on Virtual Private Servers (VPS), (C-2) achieving sufficient node selection probability for low-bandwidth VPS nodes within the Tor network, and (C-3) reliably identifying diverse and evolving threats from a wide array of IoT devices. TORCHLIGHT addresses these through a three-component architecture: the Tor Exit Traffic Collector, the Deployment Planner, and the LLM-based IoT Traffic Analyzer.
The Tor Exit Traffic Collector is responsible for real-time capture, storage, and initial filtering of external Tor traffic on resource-limited VPS nodes. This component focuses exclusively on external traffic because it remains unencrypted if application-layer end-to-end encryption is not used, making it amenable to analysis. Internal Tor traffic, conversely, is onion-encrypted and consumes significant storage. To efficiently distinguish between internal and external traffic (Solution S1 for C-1), the system leverages the observation that internal traffic involves Tor nodes for both source and destination IPs, while external traffic involves a non-Tor server as either source or destination. To manage the large number of Tor node IP addresses (over 7,000) without incurring high kernel overhead, TORCHLIGHT utilizes ipset with iptables. This allows for dynamic management of IP address sets within the Linux kernel, enabling fast lookups and efficient filtering. Rules are added to iptables to redirect relevant external traffic to NFQUEUE, where a packet sniffer captures and saves it before transmitting it to a local Network Attached Storage (NAS) via an encrypted SSH channel. Further filtering of irrelevant data is performed by excluding traffic to the Cisco Umbrella Top 1M Sites, traffic associated with hosting providers' Autonomous System Numbers (ASNs) using IPINFO data, and non-IoT specific HTTP (e.g., 5XX status codes) or Telnet (e.g., Interpret As Command sequences) responses.
The Deployment Planner (Solution S2 for C-2) optimizes the allocation of VPS resources to maximize the likelihood of observing malicious traffic, especially given the tendency of Tor clients to favor high-bandwidth nodes. By analyzing the Tor source code and its weighted bandwidth algorithm, the planner calculates the probability Pc(b) that attackers choose the deployed exit nodes to relay malicious traffic and the average time Q required. This strategy balances cost, bandwidth, and node count to achieve a desired detection probability. Algorithm 1 outlines this process: it first computes bandwidths and weights based on real-world Tor network states, then sorts node options by cost-effectiveness (bandwidth per unit price). The planner incrementally adds the most cost-effective nodes within the budget until the desired probability Desired_PC is reached or the budget is exhausted. This strategic deployment allows for cost-effective monitoring despite the limitations of low-bandwidth VPS nodes.
The LLM-based IoT Traffic Analyzer (Solution S3 for C-3) tackles the challenge of identifying diverse and unpredictable threats targeting cloudless IoT devices. It leverages large language models (LLMs) like ChatGPT (and specifically a quantized Llama 2 70B model in experiments) to process unstructured plaintext traffic. To mitigate the issue of LLM hallucination, a structured five-step Chain-of-Thought (CoT) process is implemented:
- Recognizing Device Names: The LLM, configured as an IoT domain Named-entity recognition (NER) system using in-context few-shot learning, preliminarily identifies IoT names (VENDOR, TYPE, MODEL) within response data.
- Self-Verifying for Name Confirmation: The LLM is prompted to re-verify its initial identifications to correct any hallucinated entities.
- RAG for Incomplete Name Completion: Leveraging Retrieval-Augmented Generation (RAG), the system uses the Google Custom Search API as a retriever to search for and complete missing vendor or type names based on identified model names (e.g., turning 'IPC-HFW2231S' into 'Dahua Camera IPC-HFW2231S').
- Confirming IoT Device Traffic: This crucial step distinguishes between traffic mentioning an IoT device (e.g., a blog post about a Sony camera) and traffic originating from an actual IoT device. The LLM scrutinizes the entire response to confirm the true origin, minimizing false positives.
- Analyzing Attacking Traffic: Finally, the LLM performs binary classification to detect specific attack types (reconnaissance, device manipulation, file manipulation) based on plaintext streams (e.g., HTTP requests for command injection, requests and responses for information disclosure). The detected attacks are then manually verified against threat intelligence databases like CVE and NVD, and zero-day vulnerabilities are responsibly disclosed to vendors.
Demo / Proof of Concept
While this work is presented as a peer-reviewed conference paper rather than a live demonstration, the authors rigorously validated the TORCHLIGHT system through extensive real-world data collection and subsequent vulnerability disclosures. The entire research effectively serves as a large-scale proof of concept for the feasibility and efficacy of detecting anonymous IoT attacks via Tor.
A concrete example of TORCHLIGHT's capability is the initial discovery of CVE-2024-4235, a cleartext storage vulnerability in a Netgear DG834Gv5 router. This finding, which exposed sensitive user information, directly motivated the broader research and demonstrated the system's ability to pinpoint critical flaws from observed Tor traffic.
Over the 12-month monitoring period, TORCHLIGHT processed 26 TB of traffic from three strategically deployed Tor exit relays, capturing over 60 million responses. From this vast dataset, the LLM-based analyzer successfully identified traffic from 50,874 unique IoT devices. The system's accuracy in identifying IoT devices was high, achieving 93.84% accuracy and 93.85% coverage on the collected Tor traffic dataset, with a macro average F1 score of 0.8671.
The most compelling validation comes from the 45 vulnerabilities identified, including 29 zero-day exploits, for which 25 CVE-IDs were successfully assigned. This process involved manual verification of LLM-identified attacks, cross-referencing with threat intelligence, and responsible disclosure to vendors. Examples include multiple critical OS Command Injection and Hard-coded Credentials vulnerabilities in D-Link NAS devices (CVE-2024-10915, CVE-2024-10914, CVE-2024-3273, CVE-2024-3272), and a critical Access Control flaw in Xiongmai DVR (CVE-2024-3765). The identification of specific N-day vulnerabilities like CVE-2022-28956 (D-Link Router) and CVE-2023-4474 (Zyxel NAS) further attests to TORCHLIGHT's ability to detect known exploits being actively leveraged.
To approximate attack attempts, the researchers developed custom Suricata rules for the identified vulnerabilities. Analysis of this data, as shown in Figure 7 of the paper, revealed a substantial number of exploitation attempts, peaking in June, largely attributed to the exploitation of CVE-2017-7577, a path traversal vulnerability. This detailed analysis of exploitation attempts across various vulnerabilities further solidified the practical impact of TORCHLIGHT's discoveries.
Defensive Implications
The findings from the TORCHLIGHT research carry profound implications for IoT device manufacturers, network defenders, and end-users, necessitating a multi-faceted defensive strategy.
Firstly, the prevalence of zero-day and N-day vulnerabilities, particularly in legacy and end-of-life (EOL) devices, demands immediate attention. Manufacturers must develop a more robust approach to security throughout the product lifecycle, including clear communication regarding EOL status and, where feasible, providing final security patches or migration paths. Devices like the D-Link DNS-320L NAS (with six zero-day vulnerabilities from a 2018 firmware) and the Netgear DG834Gv5 router (vulnerable since 2011) remain exposed for years, highlighting a critical gap. Defenders should conduct thorough inventories of their IoT assets, prioritizing the replacement or isolation of EOL devices that are known to be vulnerable.
Secondly, the widespread password cracking attempts observed, especially against DVRs and cameras, underscore the critical need for strong authentication mechanisms. Default or easily guessable credentials, as well as device-related passwords (e.g., "reolink", "tp-link"), are actively targeted. Users must be educated on the importance of unique, strong passwords for all IoT devices and the regular updating of these credentials. Manufacturers should enforce complex password policies and potentially implement multi-factor authentication (MFA) by default.
Thirdly, the direct internet exposure of cloudless IoT devices makes them highly susceptible. Network segmentation is a crucial defense. Organizations and even home users should isolate IoT devices on separate network segments or VLANs, limiting their ability to communicate with sensitive internal networks and reducing the blast radius of a successful compromise. Firewalls should be configured to restrict inbound and outbound traffic to only essential services and known-good destinations.
Fourthly, while TORCHLIGHT focuses on unencrypted traffic, the overall implication is that end-to-end encryption should be a fundamental design principle for all IoT communications. The study explicitly notes its limitation in detecting attacks within encrypted communication. Manufacturers should prioritize implementing robust encryption protocols for all data transmission and control channels to protect against information disclosure and manipulation.
Finally, for organizations operating Tor exit nodes or those with the capability to monitor external network traffic, the techniques employed by TORCHLIGHT offer a blueprint for proactive threat hunting. By analyzing traffic patterns for specific IP addresses, common remote service protocols (HTTP, RTSP, FTP, Telnet), and suspicious content with advanced analytics, defenders can potentially identify anonymous exploitation attempts targeting their own or their customers' IoT devices. The use of LLMs with Chain-of-Thought (CoT) and RAG demonstrates a powerful new paradigm for identifying and classifying diverse attack behaviors, which can be adapted for general network intrusion detection systems.
Key Takeaways
- Attackers actively exploit cloudless IoT devices via Tor: The research provides definitive proof that the Tor network is a significant conduit for anonymous attackers targeting directly exposed IoT devices, a previously under-recognized threat vector.
- Widespread zero-day and N-day vulnerabilities: TORCHLIGHT uncovered 45 vulnerabilities, including 29 zero-day exploits (with 25 CVE-IDs assigned), highlighting the pervasive insecurity of cloudless IoT devices and the high value of these flaws in underground markets ($312,000 estimated).
- Millions of devices at risk, especially legacy hardware: Approximately 12.71 million devices across 148 countries are affected, with DVRs and cameras being prime targets. Legacy and end-of-life products are particularly vulnerable due to lack of updates and modern security features.
- Advanced detection with LLMs: The TORCHLIGHT system effectively uses a five-step Chain-of-Thought (CoT) process with Large Language Models (LLMs) and Retrieval-Augmented Generation (RAG) to accurately identify IoT traffic and diverse attack patterns from large volumes of network data.
- Urgent need for proactive security: Defenders must prioritize patching, enforcing strong authentication, segmenting IoT networks, and implementing end-to-end encryption to mitigate risks from information disclosure, authentication bypass, and arbitrary command execution.
- Geographic and behavioral insights: The study provides insights into the geographical distribution of targeted devices (e.g., Asia, Iran leading) and attacker behaviors, such as systematic password cracking and the use of specific commands for backdoor deployment and defense disruption.
About the Speaker(s)
The research paper "TORCHLIGHT: Shedding LIGHT on Real-World Attacks on Cloudless IoT Devices Concealed within the Tor Network" was authored by a collaborative team of researchers:
- Yumingzhi Pan (Southeast University)
- Zhen Ling (Southeast University) - Also the corresponding author for this paper.
- Yue Zhang (Drexel University)
- Hongze Wang (Southeast University)
- Guangchi Liu (Southeast University)
- Junzhou Luo (Southeast University)
- Xinwen Fu (University of Massachusetts Lowell)
Their collective expertise spans various aspects of cybersecurity, network security, and potentially artificial intelligence, contributing to the interdisciplinary nature of the TORCHLIGHT project, which combines network traffic analysis, strategic deployment, and advanced AI techniques for threat detection.
Reviews
Dr. Zero (Offensive Security Researcher) — STRONG ACCEPT
Solid academic research that actually ships results: 29 zero-days, 25 CVEs assigned, 12.7M affected devices. The LLM-based traffic analysis pipeline is genuinely novel for this problem space. Not a 5-star because the Tor angle, while clever for data collection, somewhat overstates the threat model—most of these vulns are getting hammered from regular botnets too.
Heather Calloway (CISO) — SOLID
Solid research that proves attackers are using Tor to anonymously exploit cloudless IoT at scale. 29 zero-days, 12.7 million exposed devices, DVRs and cameras as primary targets. This changes how we think about IoT risk in environments with direct-exposed devices.
→ Top-rated talks at 34th USENIX Security Symposium (USENIX Security '25)
All talks from 34th USENIX Security Symposium (USENIX Security '25)